ISO/IEC 27001
Mapping to ISO/IEC 27001 controls
The platform is not ISO/IEC 27001 certified. It can, however, help your information security management system with several Annex A controls.
Contents
A clear starting point
ISO/IEC 27001 certification applies to an organization and its information security management system (ISMS), not to software. RackIntelligence is not ISO/IEC 27001 certified and does not claim to be.
What we can do is show you how the platform fits into your ISMS: which Annex A controls (2022 version) it helps implement, and what remains your responsibility. The table below serves as a basis for discussion with your CISO or your auditor.
Mapping table
| Check | What the platform brings | What stays with you |
|---|---|---|
| 5.9 Inventory of information and other associated assets | Survey of the equipment in each rack by photo (family, readable model, U position); comparison with an export of your inventory. | Inventory policy, asset owners, survey frequency, updating your inventory. |
| 5.15 Access control, 5.18 Access rights | Accounts created and deleted by an administrator; no open sign-up. | Assignment rules, periodic review of accounts. |
| 8.2 Privileged access rights | Settings and account management restricted to the administrator. | List of administrators, review of their access. |
| 8.5 Secure authentication | Temporary password to be changed, passwords stored as hashes, limited sign-in attempts, sessions that expire. | Password policy, integration with your directory if needed, to be specified within the project. |
| 8.8 Management of technical vulnerabilities | Signed releases, checked at installation; reporting channel. | Applying updates, monitoring of the host and containers. |
| 8.10 Information deletion | Deletion of an analysis from the History; automatic purge at the end of the retention period. | Retention periods, deletion of backup copies. |
| 8.13 Information backup | Data grouped on your infrastructure, in identified locations. | Backup, restore tests, retention of copies. |
| 8.19 Installation of software on operational systems | Compiled delivery in containers; signature checked at installation and at each startup launched by the installation script. | Change procedure, approval before going into production. |
| 5.23 Information security for use of cloud services | Installation on your servers; no online service required to analyze a photo. | Choice and control of hosting. |
This mapping is indicative. The applicability of each control is decided in your Statement of Applicability.
Inventory, at the heart of control 5.9
Control 5.9 requires maintaining an accurate and up-to-date inventory of assets. This is precisely the problem the platform seeks to solve: a declared inventory on one side, the field on the other, and discrepancies that accumulate between the two.
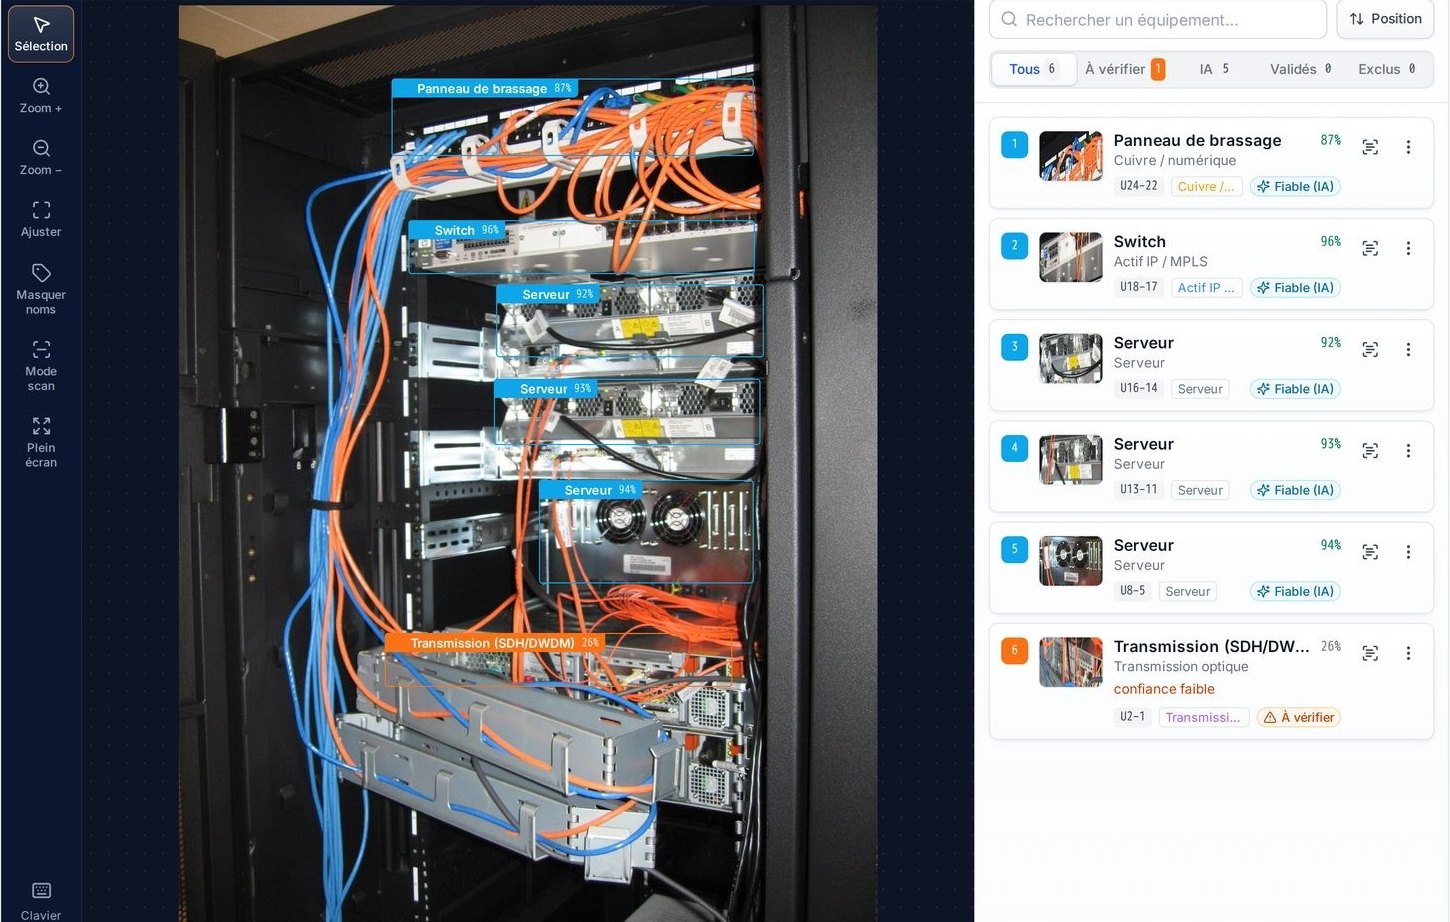
Each analysis surveys the equipment visible in the photo, with its U position and a confidence level. If the user uploads an export of your inventory to the analysis, the platform compares it with the field and distinguishes matched devices, those listed in the inventory without having been seen, and those seen without being listed in the inventory. Each analysis is dated and filed in the site’s project: you have concrete evidence to show how your inventory was checked, rack by rack.
What the platform does not cover
A tool does not replace an ISMS. Several topics remain entirely your responsibility:
- risk assessment and risk treatment;
- physical security of the rooms and servers that host the platform;
- host security: operating system, network, monitoring;
- backup and continuity, with your own tools;
- updating your inventory based on the discrepancies found;
- access review, at the frequency you set.
Preparing for an audit
If the platform falls within the scope of your ISMS, a few items make the auditor’s work easier:
Describe the installation
Servers, containers, no outbound flow: the architecture document provided as part of the project serves as the basis.
Show the access
The list of accounts, viewable by an administrator in the Users tab.
Show the analyses
Dated analyses, reopened from the History, with the engine used and its version.
Show the inventory
The inventory exported as CSV or Excel, the site report in PowerPoint and, where applicable, the comparison with your inventory file.
To get this table adapted to your Statement of Applicability, contact us.
This page describes the product. It constitutes neither a certificate of conformity nor an auditor’s opinion.